

Information Security Policy
The Information Technology Division is responsible for formulating information security policies, risk assessment, and implementation and follow-up of countermeasures. The CIO reports the implementation status to the General Manager occasionally every year. In order to reduce the risk of non-compliance and increase customer trust, we have also introduced the ISO 27001 information security management system to establish a comprehensive and systematic approach to managing and protecting the Company's information assets.
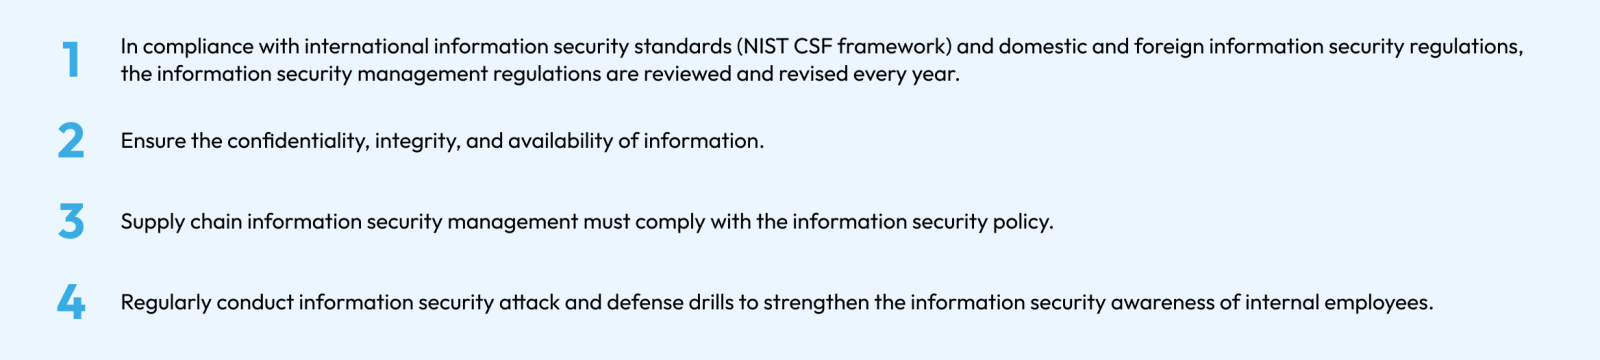
Countermeasures for Information Security
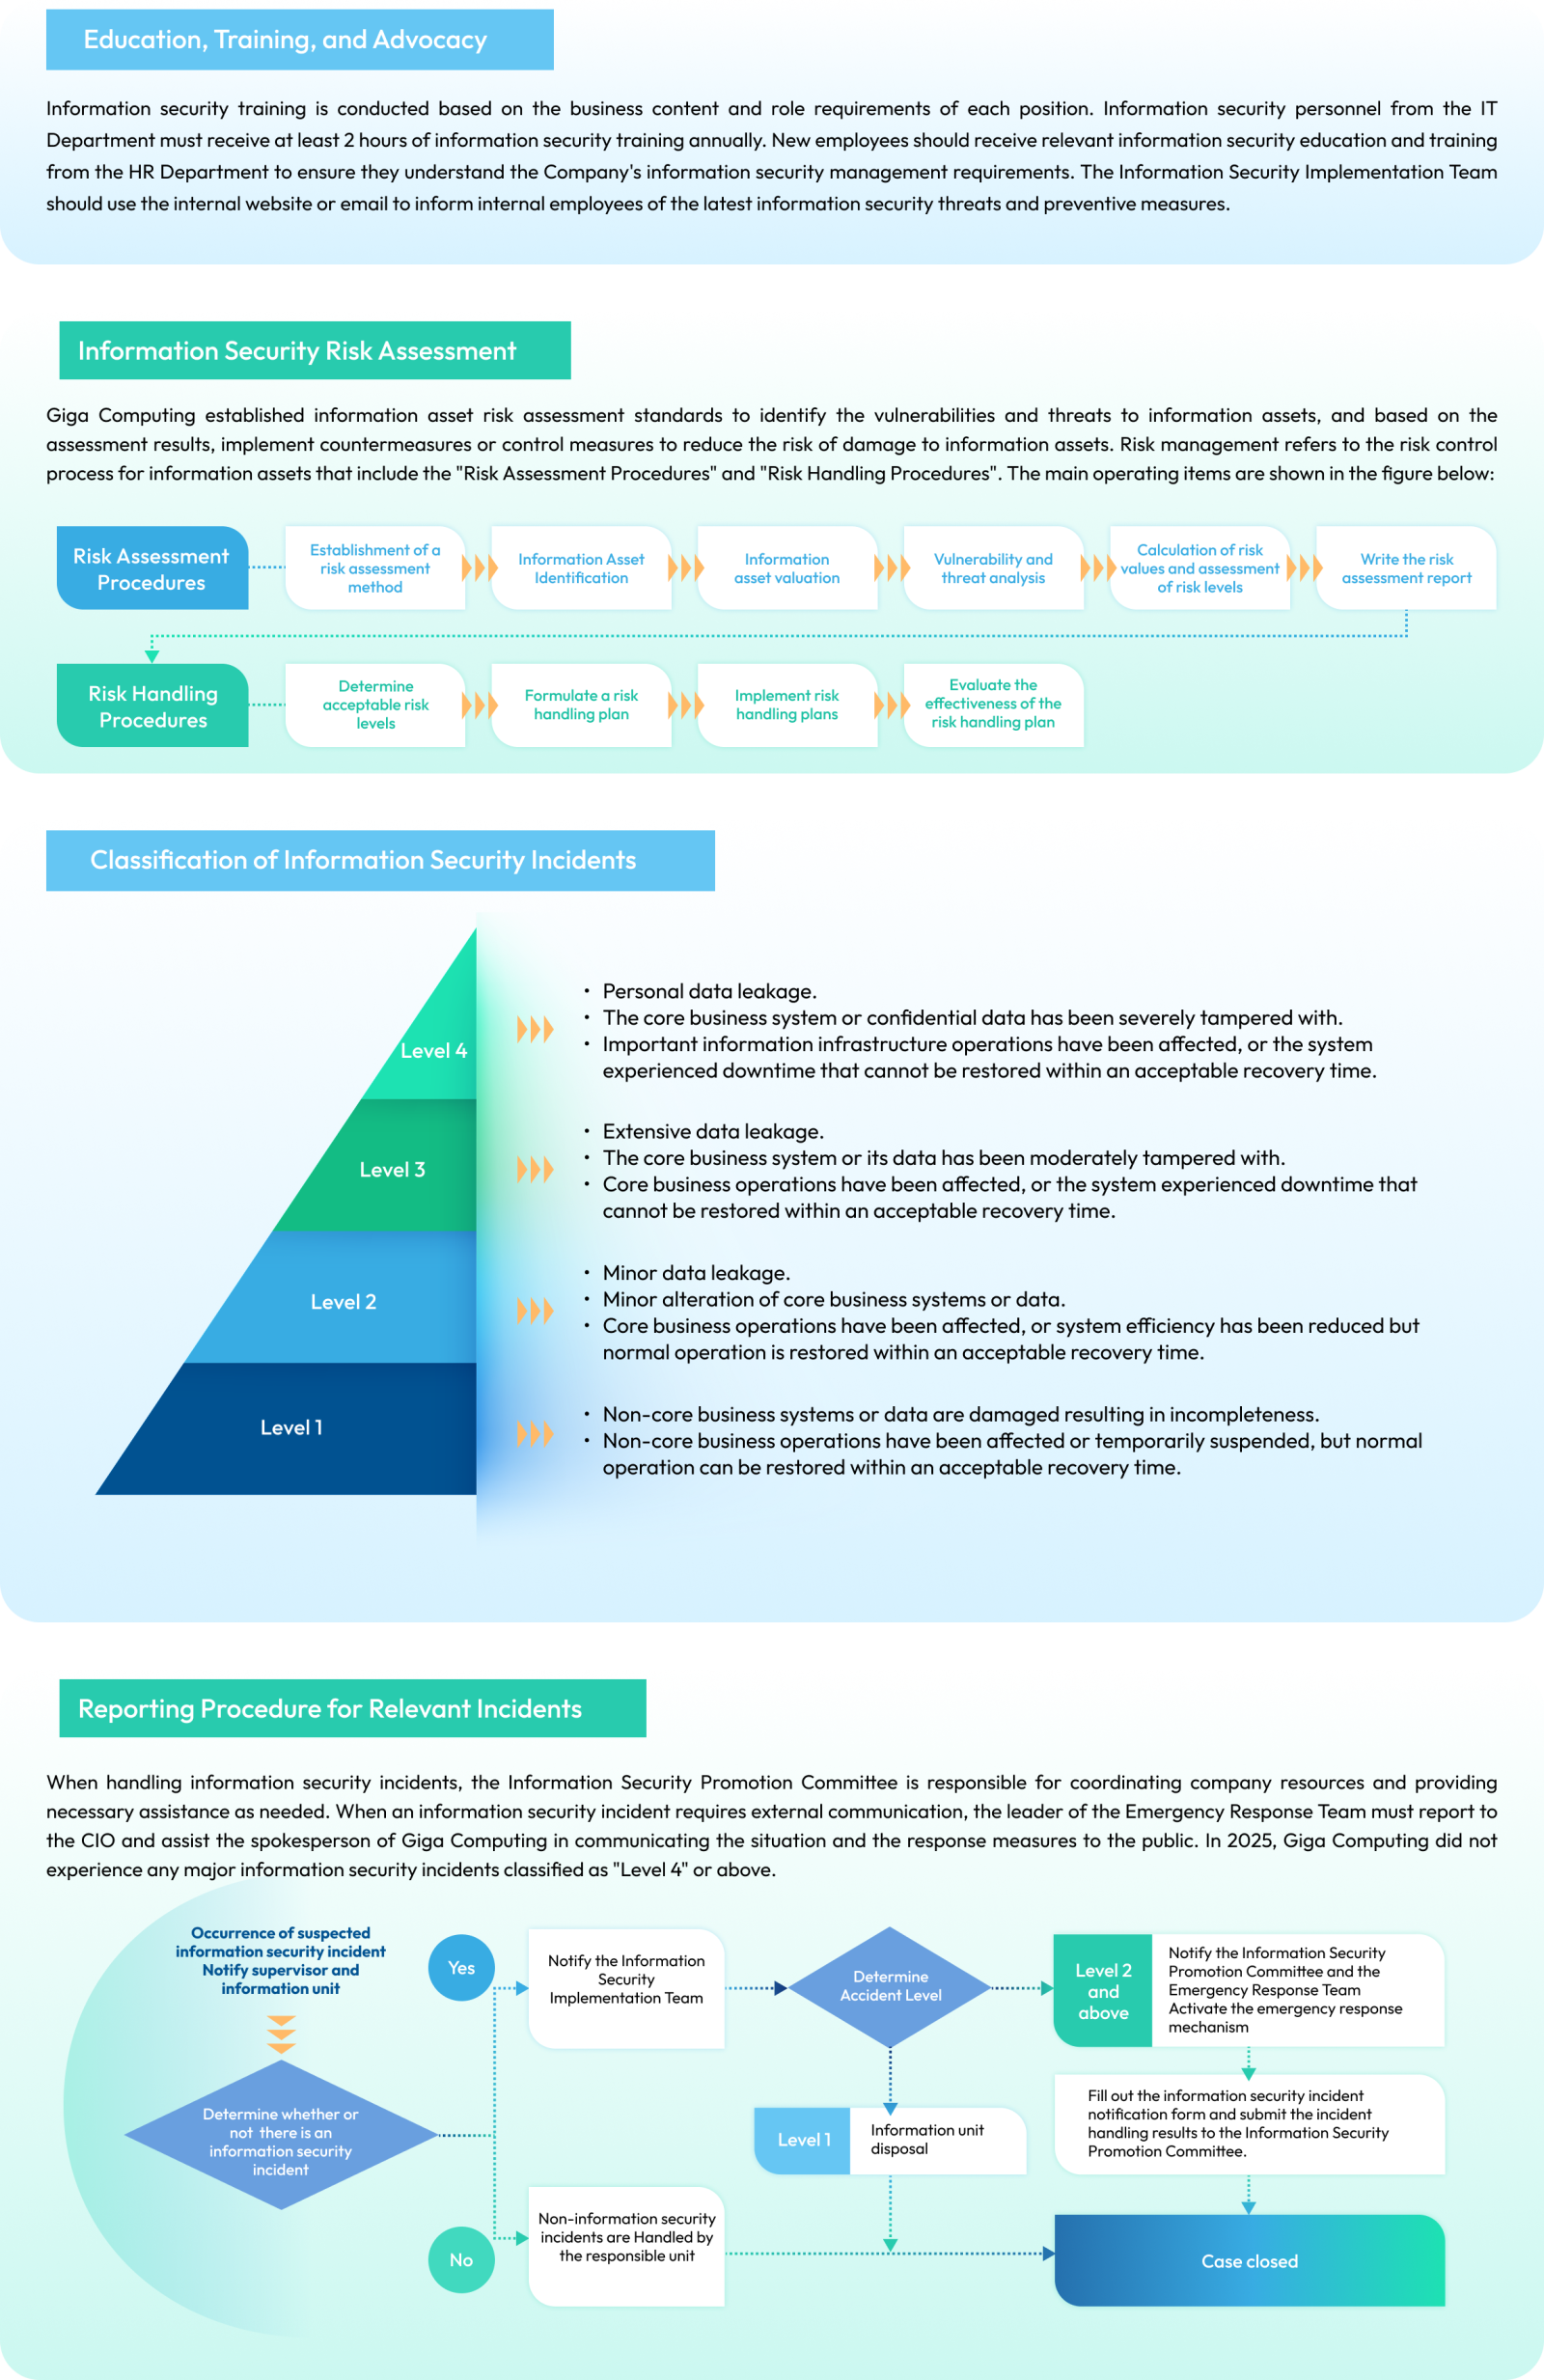
Enhance Employees' Information Security Risk Awareness
Giga Computing arranges information security education and training annually according to the business duties and roles of different positions. Information security dedicated personnel in the IT Department must receive at least 2 hours of information security education and training each year; new employees receive relevant information security education and training from the HR Department to ensure they understand the Company's information security management requirements. In 2025, the Company began conducting information security education and training for all employees to enhance employees' information security risk awareness and reduce the occurrence of information securityrelated risk incidents. A total of 2,195 attendees were recorded, with a completion rate of 88.79%. The Company aims to maintain a completion rate of over 80% in 2026 and achieve a completion rate over 90% by 2030.
To enhance employees' awareness of information security, the Information Security Implementation Team uses the internal website or email each year to inform employees of the latest information security threats and help prevent risks. In 2025, a total of 4 employee social engineering email exercises were conducted, with a click-through rate of 6%, meeting the 2025 target of less than 20%. At the same time, to address information security-related risks, starting in 2026, Giga Computing Headquarters will adopt a more stringent target and continue to conduct relevant education, training, and awareness activities with the aim of achieving a social engineering click-through rate of less than 10%.
|
Course Title |
Form of Handing | Participants | Number of People Trained | Course Hours |
Total Training Hours |
|
Information security education and training |
Physical | Information secutity personnel in the IT Department | 4 | 2 hours |
8 hours |
|
Information security awareness education and training |
Physical |
New Employee | 185 | 10 minutes |
30.83 hours |
|
Targeted Social Engineering Remedial Training |
Online | Employee who failed the drill | 80 | 30 minutes |
40 hours |
|
Information security education and training for all employees -1/3 |
Online |
All Employee | 610 | 1 hour |
610 hours |
|
Information security education and training for all employee -2/3 |
Online |
All Employee |
682 | 1 hour |
682 hours |
|
Information security education and training for all employee -3/3 |
Online |
All Employee |
657 | 1 hour |
657 hours |
|
Supply Chain Information Security Assessment Briefing |
Online |
All Employee |
73 | 1 hour |
73 hours |
| Total |
2,100.83 hours |
||||
Information Security Policy
The Information Technology Division is responsible for formulating information security policies, risk assessment, and implementation and follow-up of countermeasures. The CIO reports the implementation status to the General Manager occasionally every year. In order to reduce the risk of non-compliance and increase customer trust, we have also introduced the ISO 27001 information security management system to establish a comprehensive and systematic approach to managing and protecting the Company's information assets.
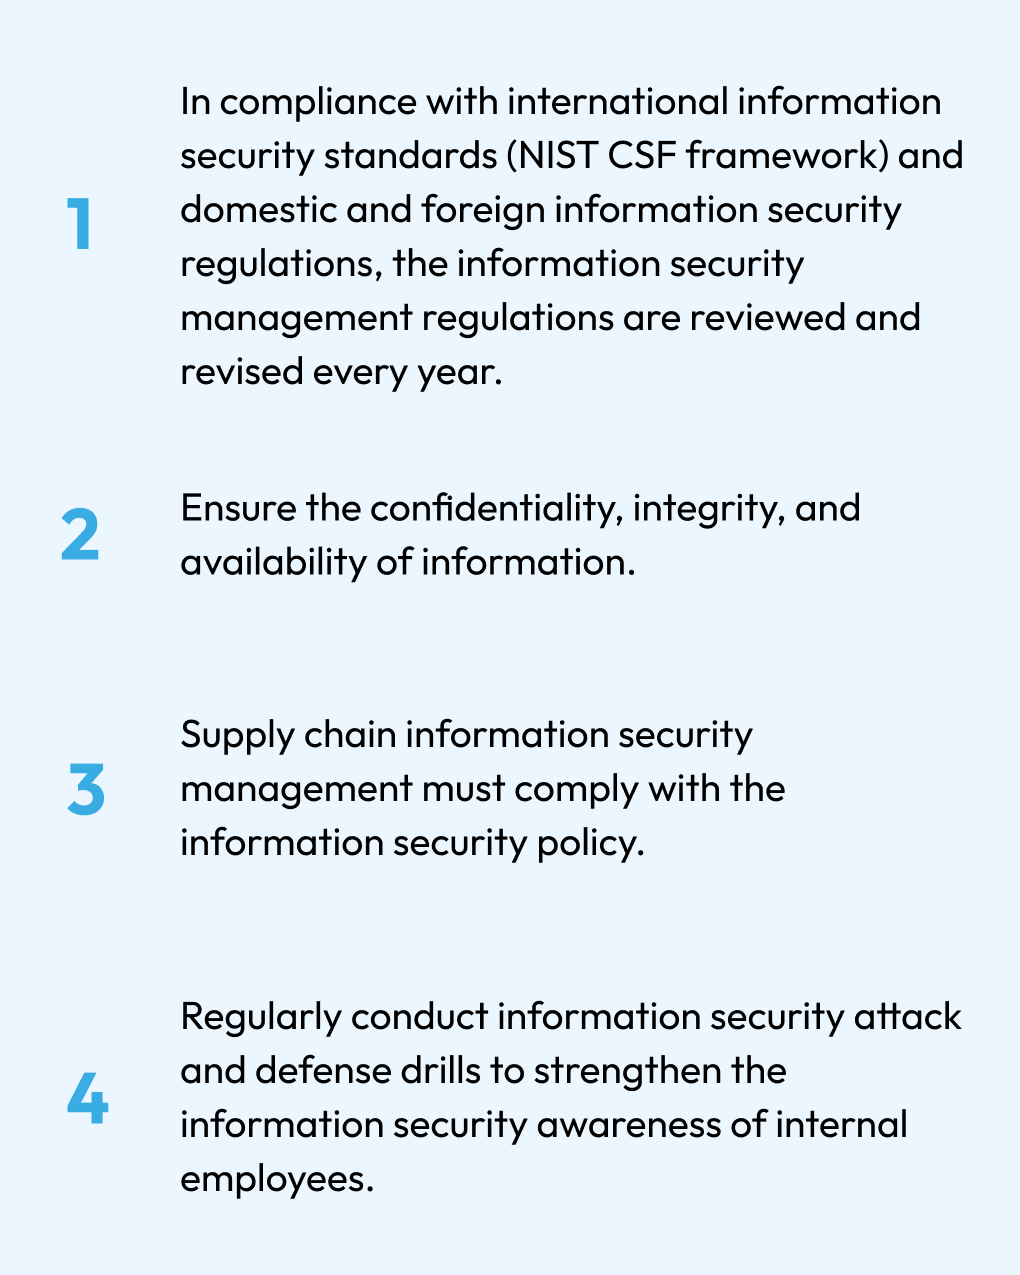
Countermeasures for Information Security

Enhance Employees' Information Security Risk Awareness
Giga Computing arranges information security education and training annually according to the business duties and roles of different positions. Information security dedicated personnel in the IT Department must receive at least 2 hours of information security education and training each year; new employees receive relevant information security education and training from the HR Department to ensure they understand the Company's information security management requirements. In 2025, the Company began conducting information security education and training for all employees to enhance employees' information security risk awareness and reduce the occurrence of information securityrelated risk incidents. A total of 2,195 attendees were recorded, with a completion rate of 88.79%. The Company aims to maintain a completion rate of over 80% in 2026 and achieve a completion rate over 90% by 2030.
To enhance employees' awareness of information security, the Information Security Implementation Team uses the internal website or email each year to inform employees of the latest information security threats and help prevent risks. In 2025, a total of 4 employee social engineering email exercises were conducted, with a click-through rate of 6%, meeting the 2025 target of less than 20%. At the same time, to address information security-related risks, starting in 2026, Giga Computing Headquarters will adopt a more stringent target and continue to conduct relevant education, training, and awareness activities with the aim of achieving a social engineering click-through rate of less than 10%.
|
Course Title |
Form of Handing | Participants | Number of People Trained | Course Hours |
Total Training Hours |
|
Information security education and training |
Physical | Information secutity personnel in the IT Department | 4 | 2 hours |
8 hours |
|
Information security awareness education and training |
Physical |
New Employee | 185 | 10 minutes |
30.83 hours |
|
Targeted Social Engineering Remedial Training |
Online | Employee who failed the drill | 80 | 30 minutes |
40 hours |
|
Information security education and training for all employees -1/3 |
Online |
All Employee | 610 | 1 hour |
610 hours |
|
Information security education and training for all employee -2/3 |
Online |
All Employee |
682 | 1 hour |
682 hours |
|
Information security education and training for all employee -3/3 |
Online |
All Employee |
657 | 1 hour |
657 hours |
|
Supply Chain Information Security Assessment Briefing |
Online |
All Employee |
73 | 1 hour |
73 hours |
| Total |
2,100.83 hours |
||||